

Manufacturing cybersecurity – assurance through research and education
24/05/2016
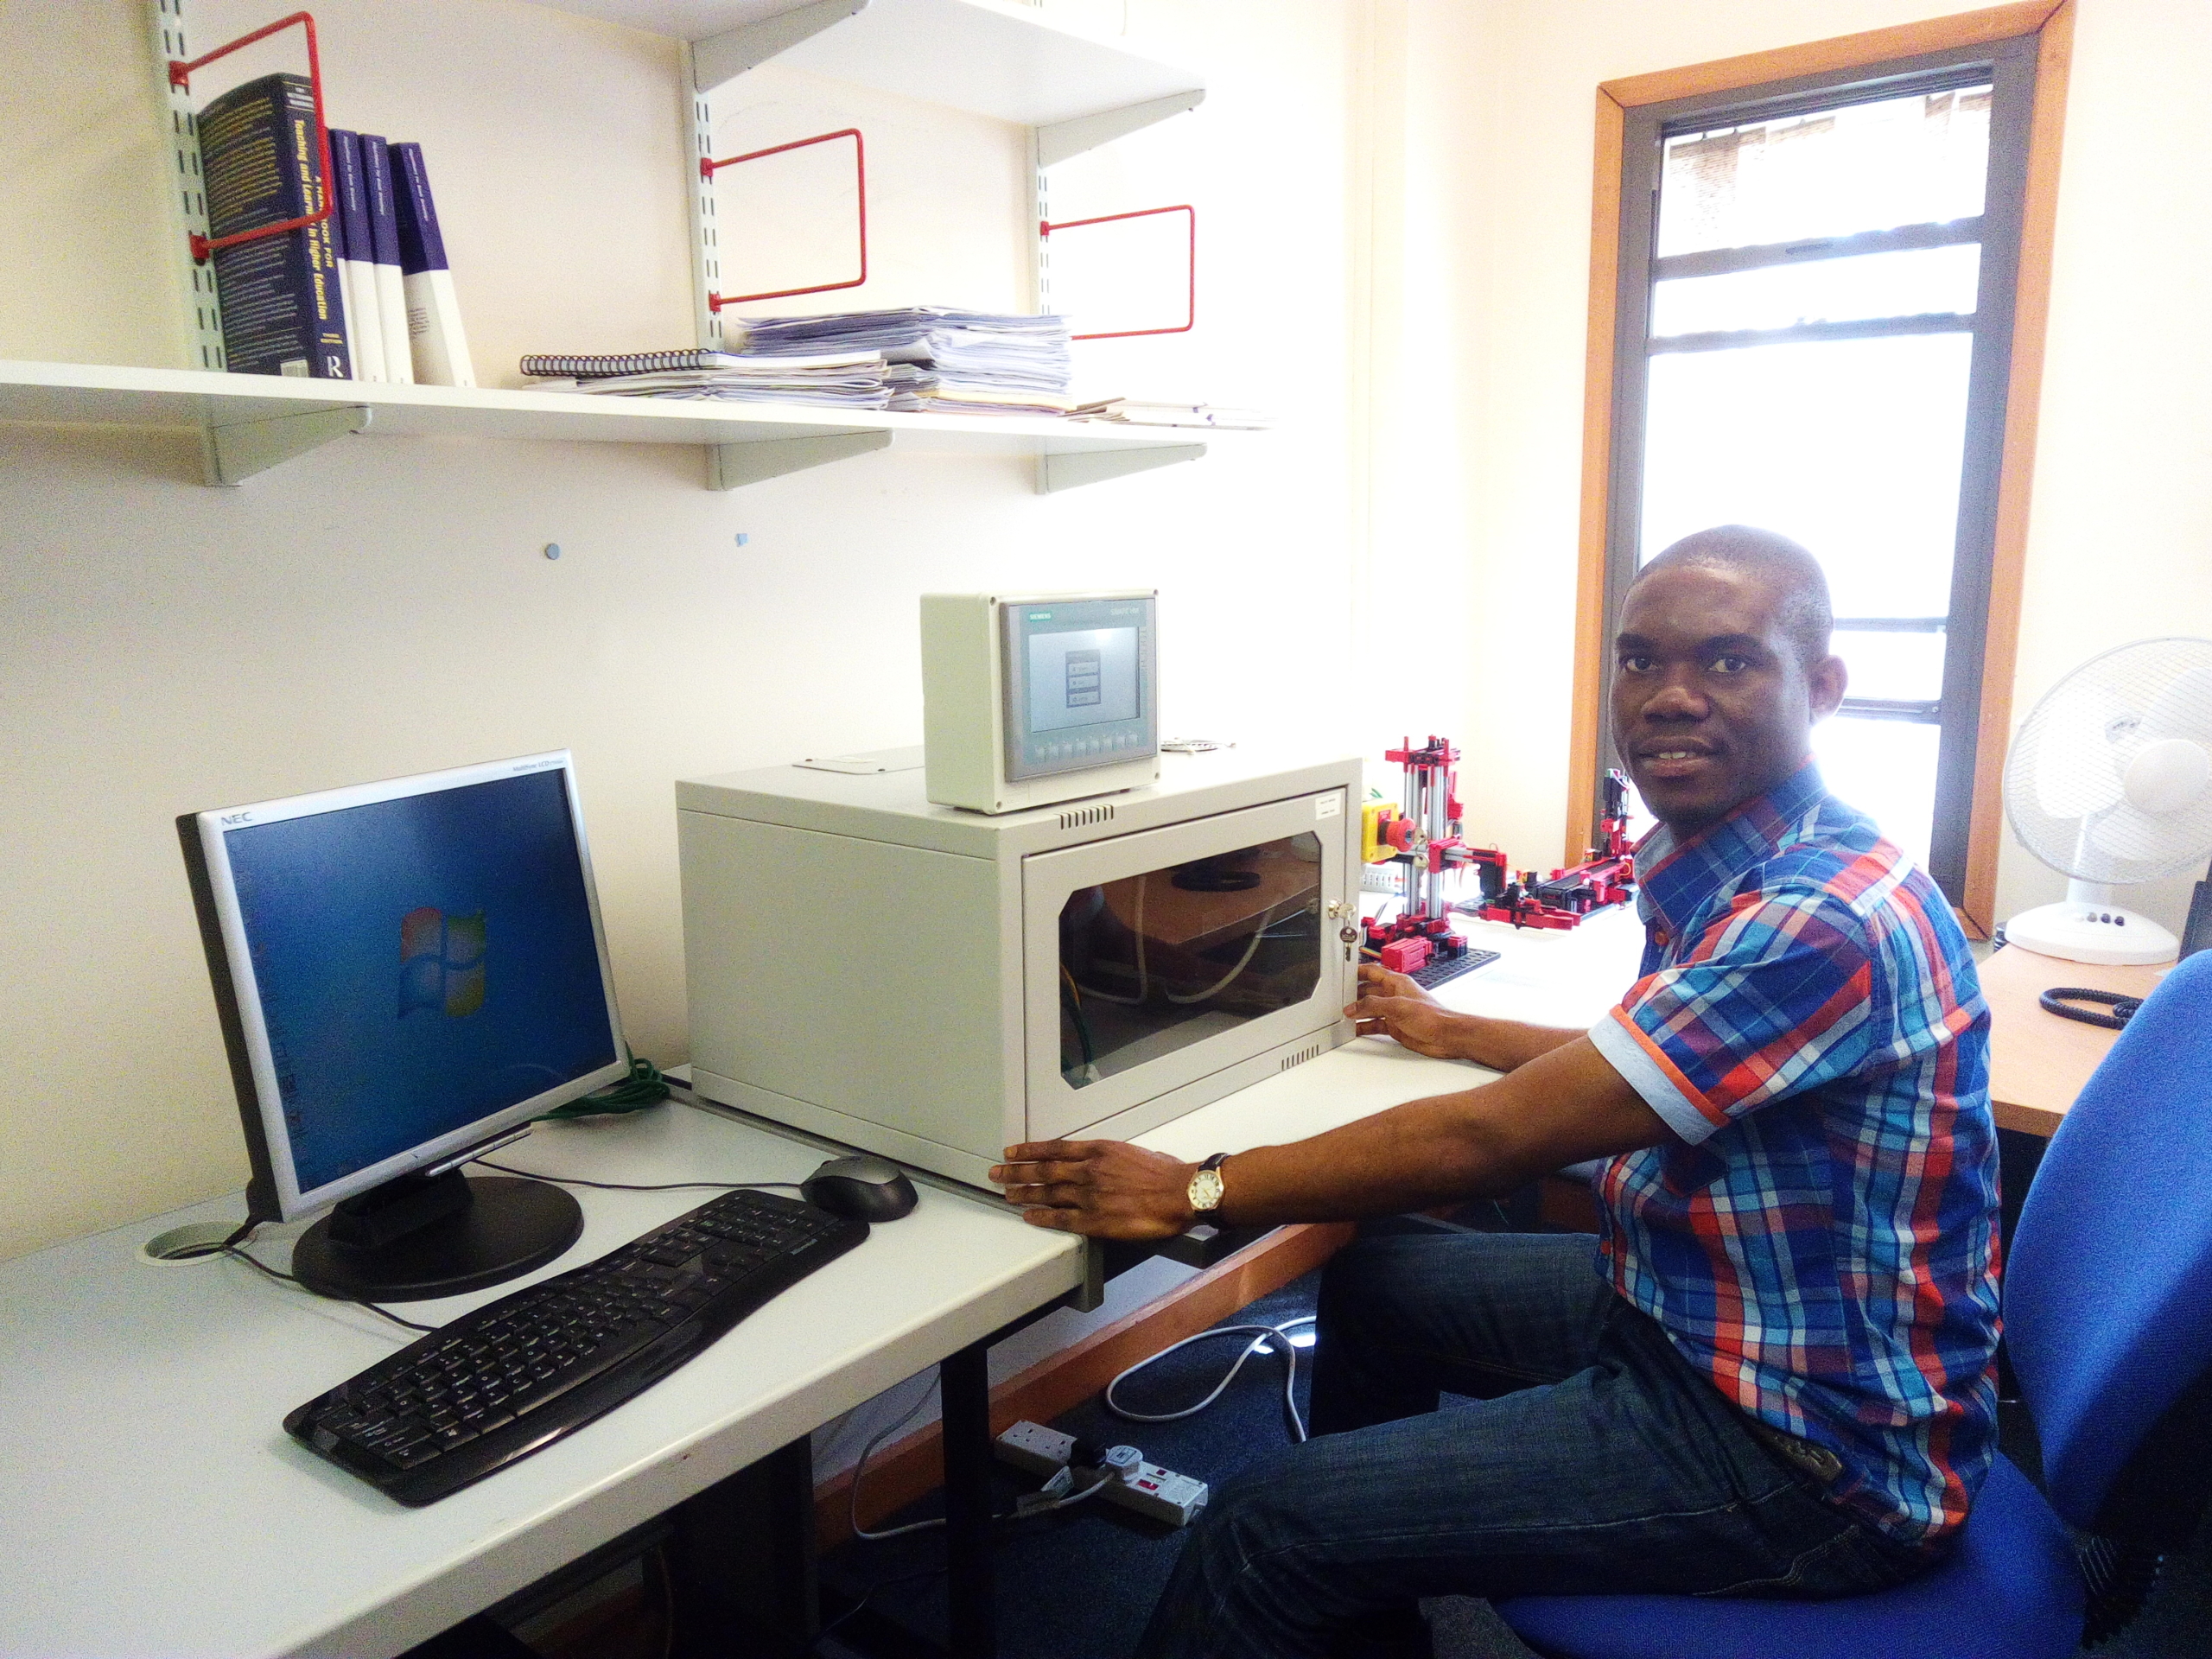
I did my first degree in computer science before coming to the UK to study a Master’s course in computer security and digital forensics. I didn’t just want to learn how to secure systems, I wanted to be able to figure out how and who was hacking. My interest in further working on protecting and improving cybersecurity systems is the reason that I decided to come to Cranfield to do my PhD.
There’s no such thing as absolute cybersecurity
The scariest thing about working in this area is that you work within the knowledge that there is no such thing as absolute security. No system is fool-proof, no platform is immune to the risks – whether it’s from competitor organisations, a disgruntled employee, terrorists, or script kids who just want to give it a go and see what they can do. The motivations vary but the risks are significant. There are couple of high profile examples – in 2014, an unnamed Germany steel mine was breached “by manipulating and disrupting control systems to such a degree that a blast furnace could not be properly shut down, resulting in “massive”—though unspecified—damage.” It was another example of a digital attack causing physical damage, following the Stuxnet virus that attacked Iran’s nuclear centrifuges.
So how is this related to our daily life? Consider the implications if there was an attack on the systems that control our water treatment network, the oil and gas industry, transportation or manufacturing infrastructure. Hacking on this kind of macro scale has the potential to cause a national and international emergency. People often worry about their personal data online or their bank accounts, as it is often followed by larger personal wealth loss.
Accepting cybersecurity as a priority
I don’t want to sound like an alarmist, but this is a realistic risk that we need to actively defend against. There is a definite need to engage proactive measures to prevent such risks. My research aims to find ways to enhance security in the light of the current demand for cybersecurity for industry 4.0, and offer solutions for companies, particularly where there is still a false sense of security. In some cases, it is believed that ‘closed’ systems aren’t vulnerable because they aren’t connected to the corporate enterprise networks or internet. But when these companies look at improving productivity and profitability by incorporating devices like routers and servers, often they aren’t aware of the risks introduced by the connection. For example, a breach could be caused by purchasing and installing vulnerable IP-enabled devices, or devices that were pre-configured with malicious software, in which case, the ‘hacking’ had happened long before the product even arrived at the company’s premises.
Can research actually help?
IoT technologies have prompted Industry 4.0, and security for smart manufacturing has attracted much attention by enterprises, organisations and researchers. Many whitepapers and reports show the significance of security with respects to enterprise systems, supply chains, connected devices, mobile devices, cloud services, and big data, etc. All of these seem dazzling to us, but provide essential clues for cybersecurity.
The security strength of an organisation depends on the degree to which organisations protect their weakest links in enterprise systems or manufacturing systems. In current security situation, people (users) could be the weakest link in an enterprise. One of my current research focuses is to develop a model for assessing manufacturing workforce cyber security capability. Essentially an evaluation method that would enable enterprise owners understand the capabilities of their workforce to preempt, detect, and respond appropriately to cyber incidents, determining the weakest link(s), specific capacity needs, and how to prioritise and engage cyber security capacity-building programmes in the manufacturing enterprise. While a testbed could provide demonstration platform for identifying and testing the cybersecurity potentials in emerging enterprise manufacturing, cyber security metrics could guide the process of identifying manufacturing infrastructure security postures and susceptibilities, and an adaptive risk management methodology for achieving manufacturing cyber security assurance.
Hence, in response to the demand for the security of smart manufacturing enabled by IoT technologies, my research will benefit the manufacturing community by: (i) improving awareness of the emerging cyber risks associated with industry 4.0 and disabusing those thoughts of being completely insulated from cyber risks; (ii) give understanding through experimental demonstrations of potential security critical control points of a manufacturing network; (iii) developing an approach to ascertaining the security capability level of both manufacturing-floor, and enterprise user workforces, thus to influence response directions for improving security; (iv) creating handy cybersecurity mixed metrics for gauging the overall security potentials of manufacturing enterprises, with appropriate risk management methodology for improving cybersecurity assurance.
What can be done to improve the awareness of cybersecurity?
The National Crime Agency’s Cyber Choices campaign aims to increase the number of young people using their coding skills positively. They point that hacking is not a victimless crime. It’s crucial that we continue to increase training and research opportunities in this area. Today, higher education is a major contributor to economic success, producing, changing and transferring cutting edge knowledge from research, and continues updating our education to match the pace of technology development. In order to respond to our continuous changing society, Cranfield manufacturing will start a new MSc Course in Cyber-Secure Manufacturing (http://www.cranfield.ac.uk/csm) in 2016/2017, to develop the next generation of manufacturing engineers who are able to protect manufacturing systems and machines against cyber threats. Correspondingly, the four core modules, as short courses, are also open to professionals in manufacturing and other engineering sectors. This is our bold step towards building security aptitude in the next generation of manufacturing and informatics graduates and experts, and also ensuring that such capacity is made available to a wider industrial and academic community.

Categories & Tags:
Leave a comment on this post:
Comments are closed.
You might also like…
5 budgeting mistakes students make (and how to avoid them)
Good financial planning isn't about how much money you have. It's about the habits you build. We asked Dr Lakshmy Subramanian, Course Director for the Banking, Economics and Finance MSc, about the budgeting mistakes ...
Finding your reading materials
Use Library Search Library Search is the first place to start when you are trying to find academic sources for your work. This is the search box on the library website homepage. It allows you ...
Formula 1 was the dream and Cranfield was the conduit
I still remember the exact moment Formula 1 (F1) got its hooks into me. I was in my first year of an aerospace undergraduate engineering degree when I watched a video about the sport ...
Introducing Barrington Library
Welcome to all our new students! Barrington Library supports all the students and staff at Cranfield Defence and Security on the Shrivenham site. We are looking forward to meeting you all soon, in person or ...
About to start your journey at Cranfield? We’re here to help!
Congratulations on accepting your offer to study at Cranfield! If you’re keen to get a head start before your course begins, our Library Services team is here to support you every step of the way. ...
Bank holiday hours for Library Services: Monday 31 August
Library Services staff will be taking a break on Monday 31 August for the bank holiday. You will still be able to access all the resources and help you need via our library website. The 24/7 ...
You are really a genius am proud to see u moving forward. Congratulations my brother. Aliyu Ibrahim OR
Excellent piece of work